Critical vulnerability in VMware vCenter allows network authentication bypass
A critical vulnerability in VMware vCenter tracked as CVE-2026-123890 received a CVSS score of 9.8. Broadcom has published patches and does not report active exploitation.
All news
RSS38 articles
- VulnerabilidadesCritical vulnerability in VMware vCenter allows network authentication bypassA critical vulnerability in VMware vCenter tracked as CVE-2026-123890 received a CVSS score of 9.8. Broadcom has published patches and does not report active exploitation.By CyberX I.T Solutions
 CibersegurançaN-able suffers cloud server breach, impacting email securityN-able confirmed that unknown actors accessed a Mail Assure and SpamExperts cloud server, disabling management interfaces globally.By CyberX I.T Solutions
 CibersegurançaAI pentesting gains momentum, but data privacy and production security remain top concernsA survey by Intruder reveals that 55% of organizations already use AI-driven pentesting, while 40% cite data privacy and 36% production security as the main barriers.By CyberX I.T Solutions
 CibersegurançaEggStreme malware rewritten to evade detections in government attacksChina-linked APT group redesigned the EggStreme framework with new network architectures, encryption, and passive mode to bypass security tools.By CyberX I.T Solutions
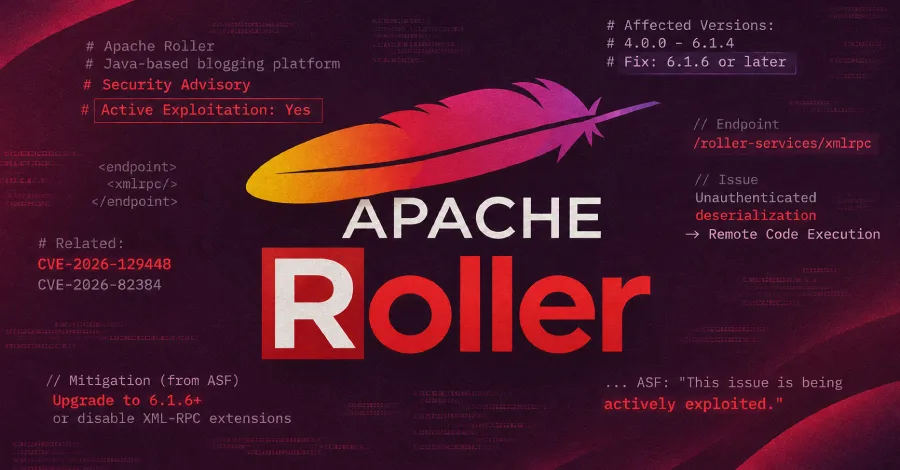 CibersegurançaCritical remote code execution flaw in Apache Roller actively exploitedThe vulnerability CVE-2026-129448 affects the Apache Roller platform, allowing unauthenticated remote code execution via the XML-RPC endpoint.By CyberX I.T Solutions
 CibersegurançaF5 warns of six critical vulnerabilities in BIG‑IP that can cause TMM crash and enable RCEF5 disclosed six critical flaws in BIG‑IP that allow crashing the Traffic Management Microkernel (TMM) and, in some scenarios, executing remote code. The company released engineering hotfixes without guaranteed functionality.By CyberX I.T Solutions
 CibersegurançaHTTP/2 Vulnerability in NGINX Allows Unauthenticated Code Execution (CVE‑2026‑123007)A flaw in NGINX's HTTP/2 support dating back more than a decade (CVE‑2026‑123007) allows unauthenticated attackers to execute code on affected servers.By CyberX I.T Solutions
 CibersegurançaTPM Firmware Flaw Reduces PIN Cracking Time on AMD and Intel PCsResearchers demonstrate that, by opening a PC's case, it is possible to rewrite the TPM state and bypass the PIN attempt lockout in Windows Hello and BitLocker, reducing the time to discover PINs from years to days.By CyberX I.T Solutions
 CibersegurançaPentesting with AI: How to Choose Vendors in an Accelerated Exploitation ScenarioThe increasing speed of vulnerability exploitation, driven by AI, demands a more rigorous approach to selecting autonomous pentesting tools. Evaluating vendors in real-world environments is crucial to ensure coverage and security.By CyberX I.T Solutions